Security
Built for card data from the first line of code
Cardvoy holds card numbers, customer IDs and the custody chain of physical cards. These are the controls that protect them, and how an auditor can test each one.
Card numbers
Tokenised with an HMAC and encrypted with AES-256-GCM on arrival, with a key per bank. Staff see a masked number. A full number is shown only when two people approve it, and every reveal is audited.
Audit trail
Each bank has its own hash-chained audit trail. Every entry includes the hash of the one before. The database refuses updates and deletes, and the chain can be verified from the screen at any time.
Maker-checker
Holds, hot-marking, destruction, re-dispatch, configuration and role changes need a second person. The server refuses a checker who is the maker, and segregation-of-duties rules stop conflicting roles.
Sign-in
Passwords hashed with PBKDF2 (210,000 iterations), authenticator-app MFA (required for administrators by policy), account lockout, idle timeout and an IP allow-list per bank.
Bank isolation
Every record carries its bank, and every request is checked against it. A session from one bank cannot read another bank’s data, which the API tests verify on every build.
Integrations
Scoped API keys stored only as hashes; IP allow-lists; courier webhooks signed with a separate secret, time-limited and protected against replay.
Transport and hosting
TLS 1.2+ everywhere, strict security headers and content security policy, a web application firewall on AWS, and database connections over verified TLS.
Logs
Structured logs with card numbers, tokens, passwords and one-time codes redacted before they are written.
Licensing
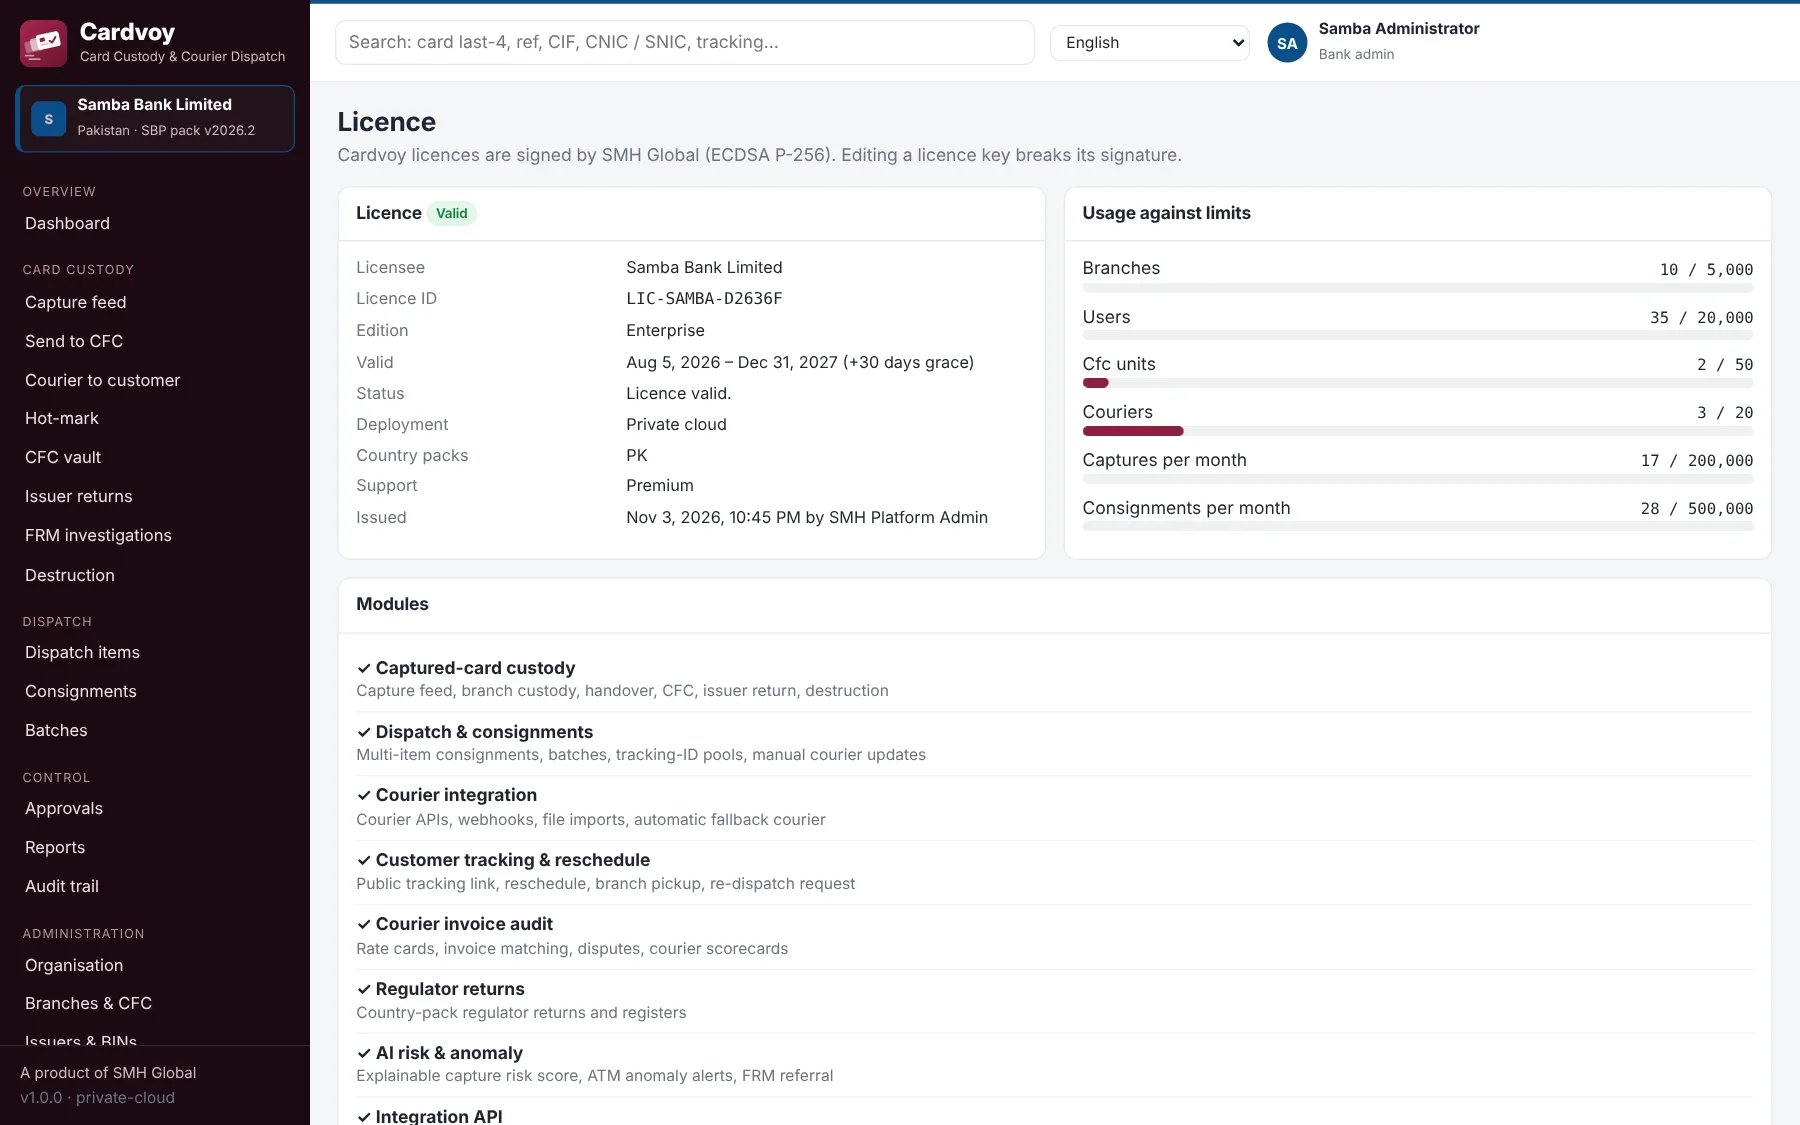
Licences are signed with ECDSA P-256. An expired licence switches the system to read-only after its grace period; data is never locked away.
Honest about limits
What comes next
An independent code review of v1.0 was completed in November 2026. Its findings were fixed or are scheduled above with interim controls in the runbook.
- Database row-level security and a least-privilege database role (v1.1)
- Externally anchored audit hashes on write-once storage (v1.1)
- Single sign-on with Azure AD, Okta, ADFS and LDAP (v1.1)
- Automated master-key rotation (v1.1)
- Independent penetration test before the first production go-live
See Cardvoy with your own process.
Book a walkthrough: we configure your branches, CFC, couriers and country pack in a private POC and run a captured card from ATM to customer while you watch.